Address various types of fraud with a coordinated strategy
Fraud vectors evolve constantly, and no single tool can catch every threat in isolation. Real-time contact validation provides essential front-line defense at entry, while behavioral analytics, step-up authentication, and transaction monitoring safeguard later stages of the customer journey.
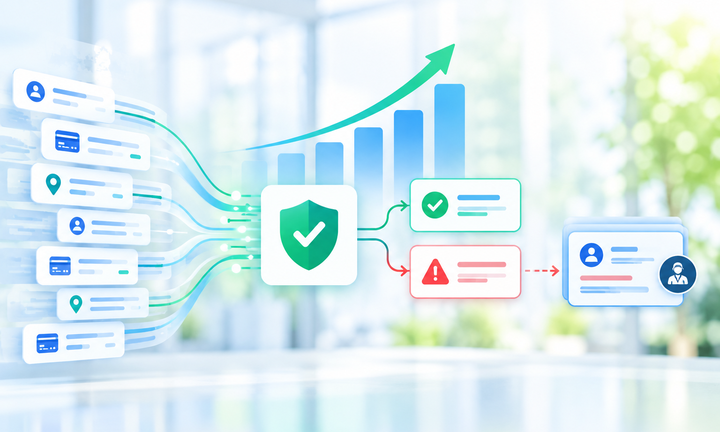
Integrating Byteplant’s Anti-Fraud API into your broader security architecture connects these layer defenses. By cross-referencing verified contact signals and providing intelligent aggregate risk scoring, your platform can spot subtle discrepancies across channels, isolate complex attack patterns, and neutralize threats before losses occur.
Common types of fraud: Fake sign-ups, bonus abuse and identity theft
Fraudsters may create multiple accounts to claim welcome offers, combine genuine and fake details into synthetic identities, or use information obtained through identity theft. Their target may be promotional credit, goods or execute transactions using stolen credentials.
Byteplant’s Anti-Fraud API exposes these vulnerabilities in real time by flagging disposable emails, high-risk phone numbers, and IP anomalies at entry. Cross-referencing these validation metrics with your own internal data creates a multi-dimensional risk profile—allowing you to intercept abusive accounts automatically while preserving high approval rates for genuine customers.
Detect suspicious behavior around account access
Social engineering can persuade customers or staff to disclose credentials or approve unauthorized changes. Once malicious parties gain account access, they may replace recovery details, redirect deliveries or initiate transactions.
While behavioral analytics and login monitoring track unusual access patterns or device switches, Byteplant’s Anti-Fraud API provides vital front-line context. By evaluating and cross-checking newly submitted addresses, emails, and phone numbers in real time, the Anti-Fraud API instantly flags high-risk changes—such as disposable emails, unassigned phone numbers, or geographic mismatches—triggering step-up re-authentication before unauthorized updates take effect.
Improve fraud detection with machine learning
Machine learning models can use historical data to identify relationships across transactions, account activity and other signals. Validated contact information gives these algorithms more consistent inputs and can support the development of more useful risk assessments.
AI models need reliable training examples, testing and ongoing monitoring. Review confirmed cases, research emerging techniques and evaluate model performance as customer behavior changes. Regular updates help models remain useful as fraud patterns evolve. Combined with clear rules and human review, this helps organizations adapt their solutions and keep false positives under control.
Educate employees to support fraud prevention
Technical checks work best when staff understand the decisions around them. Educate employees to recognize social engineering, question unusual requests and follow clear escalation procedures. Every employee who can change customer records or approve transactions should know when additional verification is required.
Training should also cover how to handle sensitive data and record the evidence behind a decision. Automation can remove repetitive checks while experienced staff investigate complex cases, communicate with customers and refine the procedures that protect the business.